

Magento Jiří Brada 4 min read
Meet Magento Germany 2026: what I brought home from a conference in a pyramid
Last week the organizers invited me to speak at Meet Magento Germany. What the event is, why I love going to Meet Magento, and what it means for your online store.

On Thursday, October 22, the Magento community gathered in Mainz for Meet Magento Germany.[1] The organizers invited me to give a talk on online store security, and I spoke in the main hall. There was no direct flight and the railway was under maintenance, so I drove from Brno. It was worth it.
What Meet Magento is
Meet Magento is a series of conferences about Magento, an open‑source platform for online stores, held around the world: New York, Florida, London, Italy, France, Poland and Prague. It all started in Germany in 2009.[1] The events bring together store owners, agencies, developers and module authors. At the end of the summer I also had the chance to speak at Meet Magento Czech in Prague. This year I was also invited to speak in Florida, but sadly it does not fit into my schedule.
Magento is owned and developed by Adobe, but the community of developers and companies around it is huge. They find bugs, write modules and share what works. That is the strength of open source: you are never on your own. And what gets discussed at these conferences today is what your store feels a few months later.
It is all about people
This year the conference returned to Germany after many years, straight into the Pyramid in Mainz. The program ran on four stages at once,[1] but the best part happened between talks. At the tables, people discussed everything from late‑night server updates to how their teams work with AI.
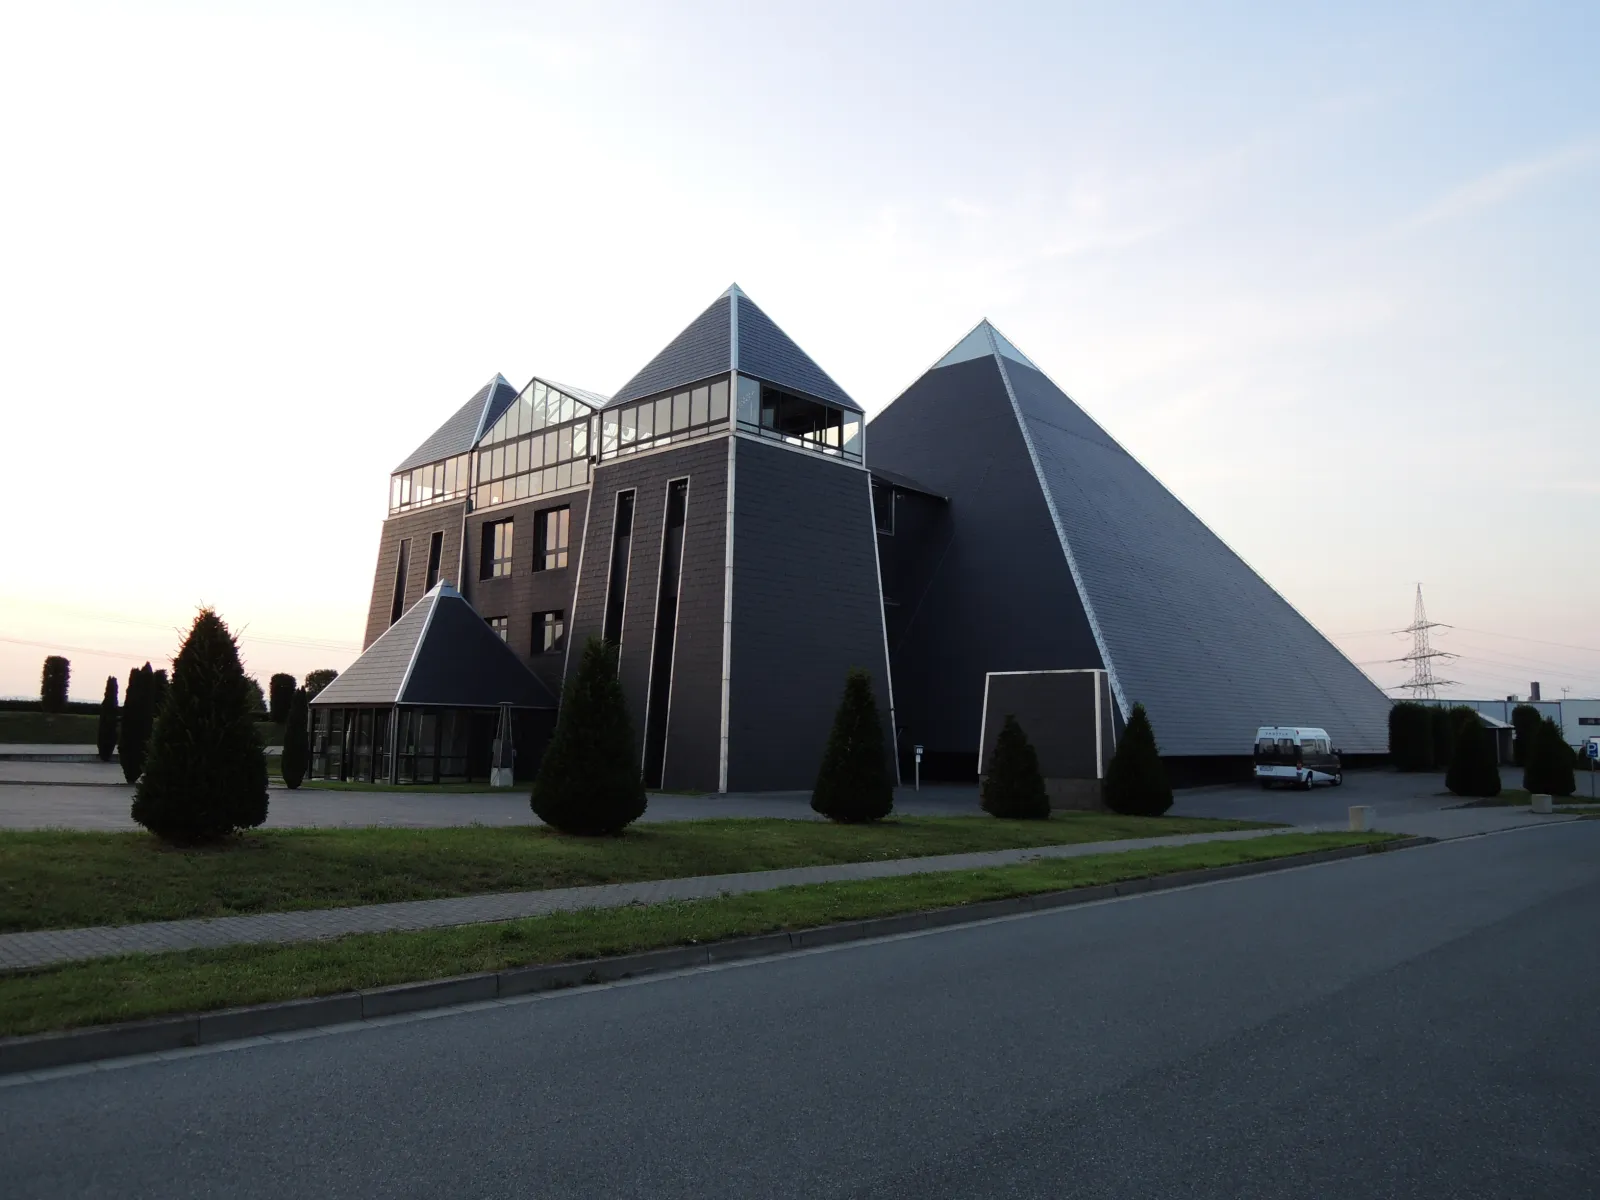
The Pac‑Man rule worked well: when you stand in a group, leave a gap in the circle so anyone can join. In the evening we moved all the way up to the tip of the pyramid, and the conversations carried on over German beer. Sadly, there was no Czech beer on tap, but I survived.
My talk: ownership is not just an advantage, it is a responsibility
In the main hall I opened a topic that often gets pushed aside in e‑commerce: security. Open source gives merchants freedom and control over their own store. But that comes with responsibility. Security updates, the modules you use, the infrastructure and the way changes get deployed all directly affect the security of the whole store. Even good hosting is not enough on its own.
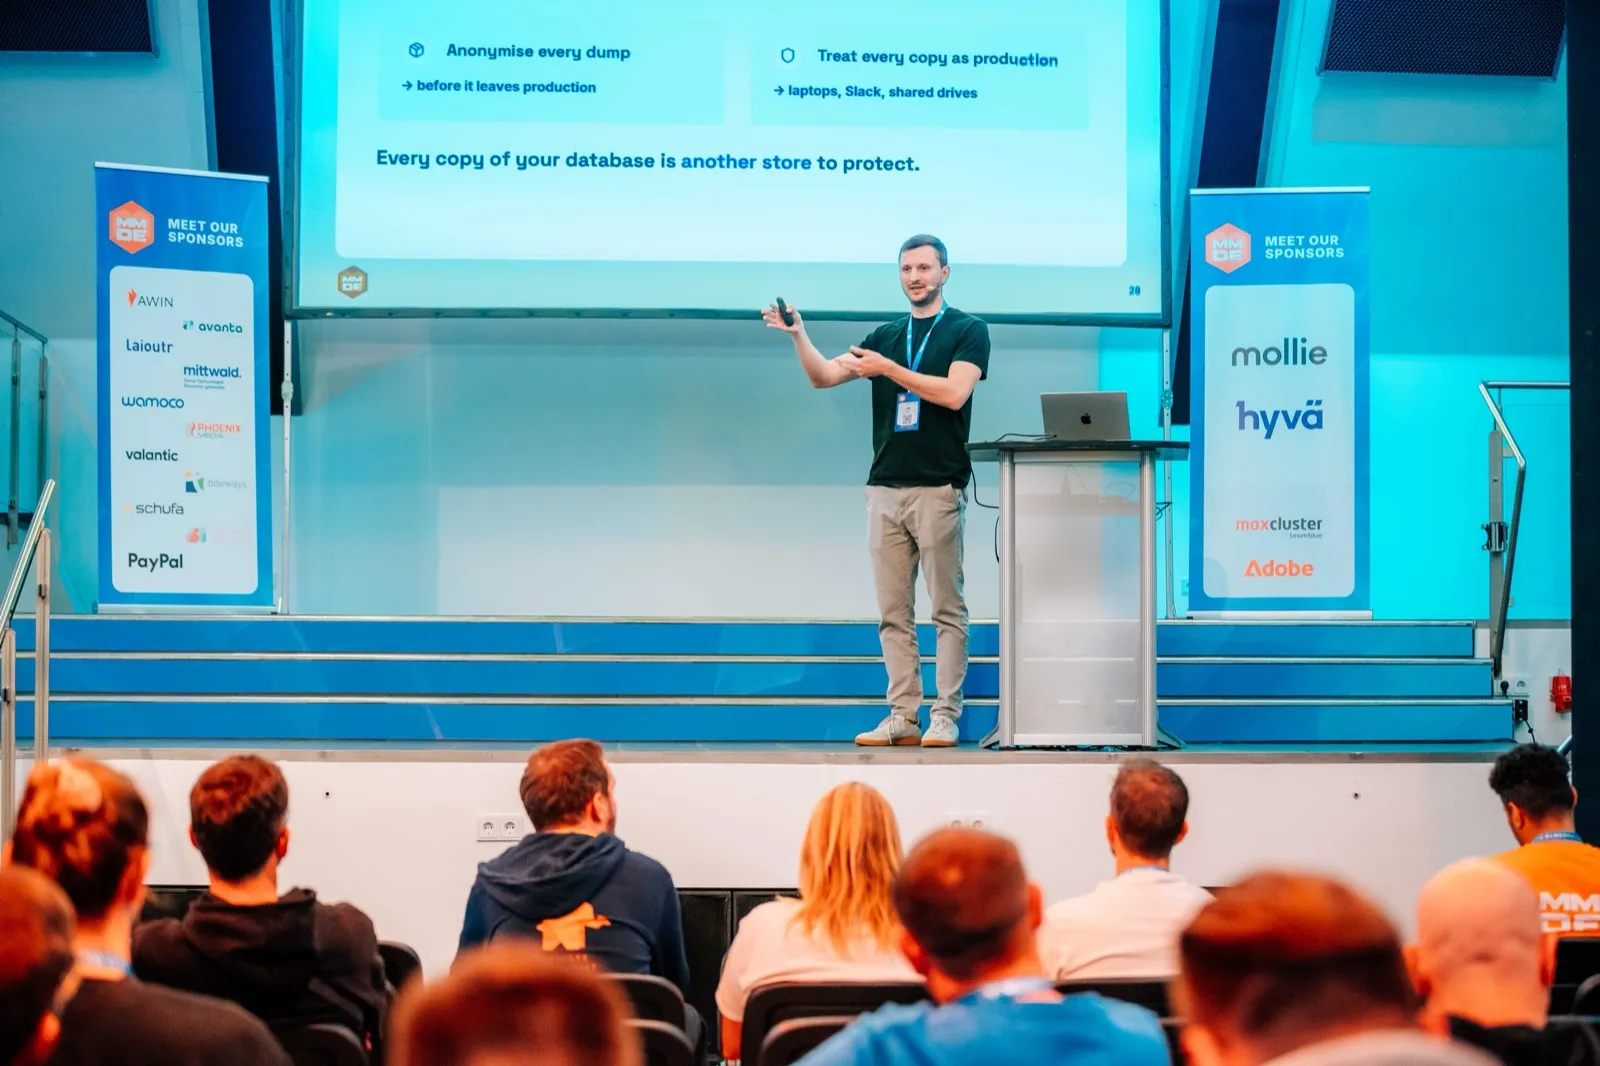
That is why updates should be a boring routine. Here, boring is the highest praise.
One number says it all: of almost 27,000 Magento stores I checked, nearly one in five has not even installed the July security fix.[2] Yet attackers can now exploit a new flaw within days.[3] I explained how Magento fixes are released in How Magento releases work.
I closed the talk with a line I stand by: in the feature race, you lose slowly. In security, you lose everything at once.
The hallway talk: a critical flaw in PHP
The day before the conference, emergency fixes came out for two critical flaws in PHP, the language Magento is written in. They let an attacker take over a server without logging in.[4] Sansec, a company that has focused on Magento security for years, warned in advance that it expected mass attacks within 15 minutes of the fixes going public.[5] It later toned that estimate down,[6] but it still shows how little time there is to update. Plenty of people in the room had spent the night before updating servers. The news caught me on my way to the conference, and I wrote a short post about it on Instagram.
On top of that, the fixes came out only for PHP 8.2 and newer.[4] Anyone running a store on an older version now has a real problem.
AI: opportunity and risk
AI came up at every turn. One talk asked whether ChatGPT will recommend your store, since some shoppers now ask a chatbot instead of Google. One interesting finding: the llms.txt file that gets written about a lot is barely read by AI tools so far. robots.txt matters more, meaning whether you let AI onto your site at all.
Other talks shared hands‑on experience with AI agents that write code. They can be brilliant and then badly wrong, so their work needs watching. And the Mage‑OS team, behind a community version of Magento,[7] showed their own AI assistant, Mago.
What it means for your store
- Ask your developer when they last installed a security fix.
- Find out which PHP version your store runs on. Older than 8.2? Plan the upgrade.
- Agree on who watches for fixes and how soon they get installed.
- Have modules and features you do not use removed. Code your store does not run cannot be exploited.
And at Deedhold?
Here, this is not your problem. We believe merchants should not have to choose between the freedom of open source and peace of mind. That is why we watch for and install Magento and PHP security fixes for you, emergency ones as soon as they come out. Every store is protected by a firewall, security monitoring and a daily malware scan. And what we bring home from conferences goes straight into how we look after your store. Technology should help your business, not distract from it. How we protect stores
Why I go to Meet Magento
From the Czech Republic and Slovakia, I am usually the only one at these conferences. That is a shame, because you never learn as much as you do straight from the community. And it works both ways: what I learn or what we build at Deedhold, I am happy to pass on, whether on stage, over a beer or here on the blog.
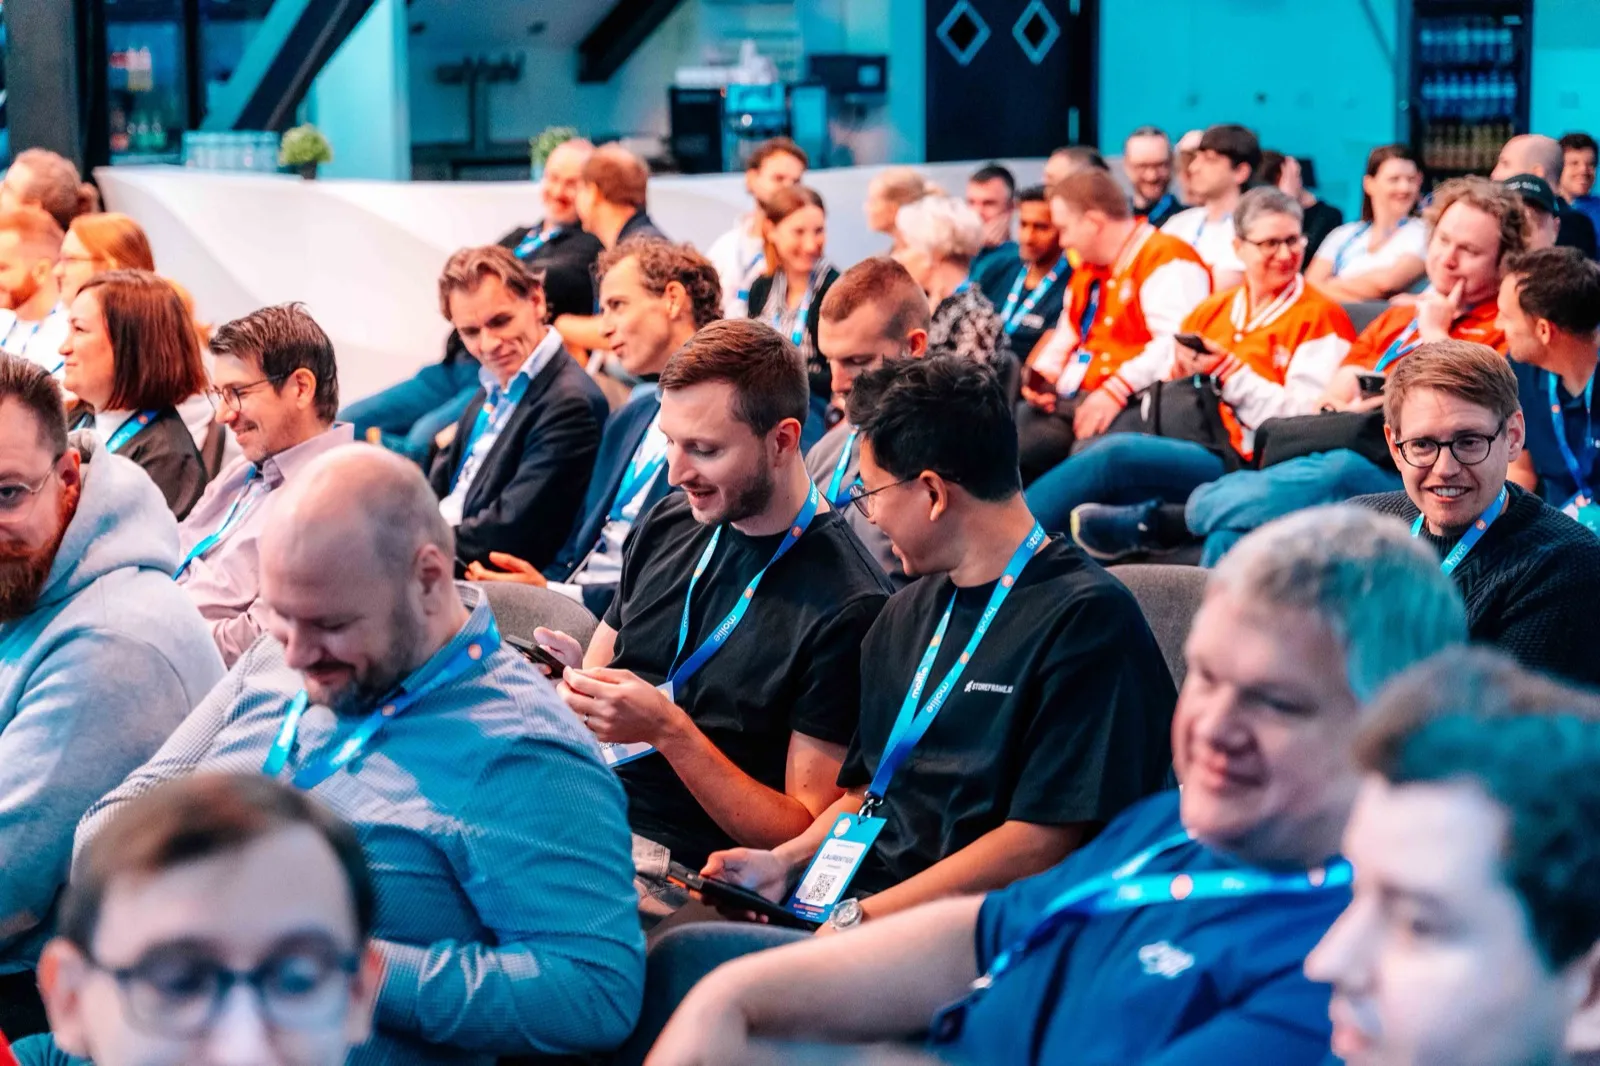
If you were not there, you missed out.
Sources
- Meet Magento Germany 2026: de.meet-magento.com (accessed October 27, 2026)
- Author's own measurement presented at Meet Magento Germany 2026: rollout of isolated Magento security fixes (APSB26-73, -92, -146, -153) across 26,786 stores as of October 22, 2026.
- How Low Can You Go? An Analysis of 2023 Time-to-Exploit Trends, Google Cloud: cloud.google.com (accessed October 27, 2026)
- Security advisory: Critical remote code execution vulnerabilities, update now, PHP: php.net (accessed October 27, 2026)
- PHP2Shell Is Coming: Your Patch Window Is 15 Minutes, Secure in Seconds, October 21, 2026: secureinseconds.com (accessed October 27, 2026)
- PHP2Shell: PHP RCE (CVE-2026-109618, CVE-2026-109619), Sansec: sansec.io (accessed October 27, 2026)
- Mage-OS: mage-os.org (accessed October 27, 2026)
